•SiTech AI Team
Tensorlake npm Package Compromised to Deliver Shai-Hulud Credential-Stealing Worm
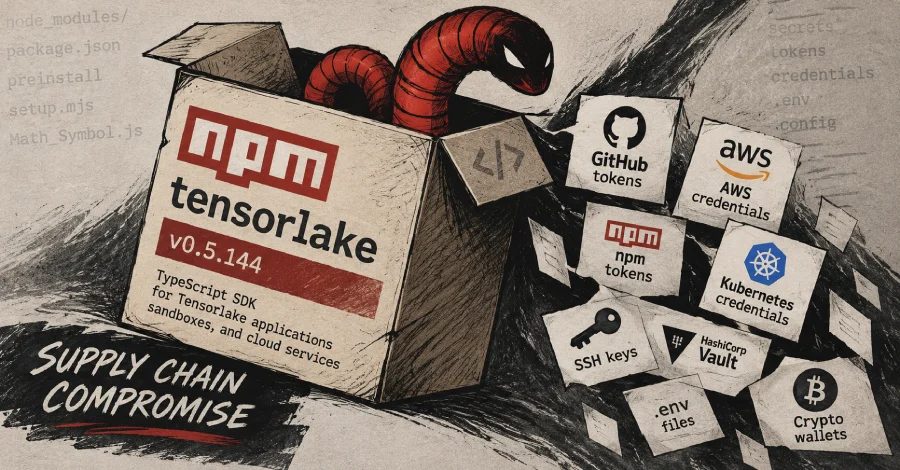
The npm package tensorlake, a TypeScript SDK, was compromised in a ChainDrop supply chain attack. Malicious version 0.5.144 delivered a self-propagating credential-stealing worm targeting npm, GitHub, AWS, Vault, and Kubernetes secrets.