Blog
Articles about web development, AI, and technology
60 articles · 14 tags · 14 connections
Drag · tap a tag to filter articles
2 articles · Page 1 of 1
•SiTech AI Team
Microsoft's official Python agent framework hijacked to distribute malware
Microsoft's official agent-framework package on PyPI has been hijacked to install info-stealing malware, researchers say, with versions 1.26.1 and 1.26.2 exfiltrating credentials and tokens.
•SiTech AI Team
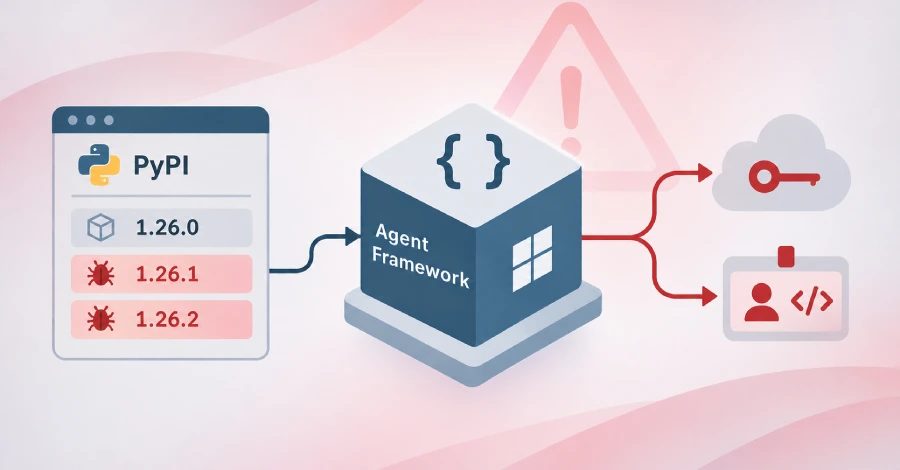
Attackers Compromise Microsoft's Agent Framework PyPI Package to Steal Cloud Credentials
Malicious versions 1.26.1 and 1.26.2 of Microsoft's agent-framework PyPI package ran a credential stealer on every Python start and exfiltrated cloud credentials to a webhook endpoint.