Blog
Articles about web development, AI, and technology
60 articles · 17 tags · 23 connections
Drag · tap a tag to filter articles
2 articles · Page 1 of 1
•SiTech AI Team
UAC-0099 Deploys ASHVEIN RAT Against Ukrainian Government Targets
Russia-aligned threat actor UAC-0099 has been linked to a new .NET infostealer and remote access trojan called ASHVEIN, used in attacks on Ukrainian government personnel.
•SiTech AI Team
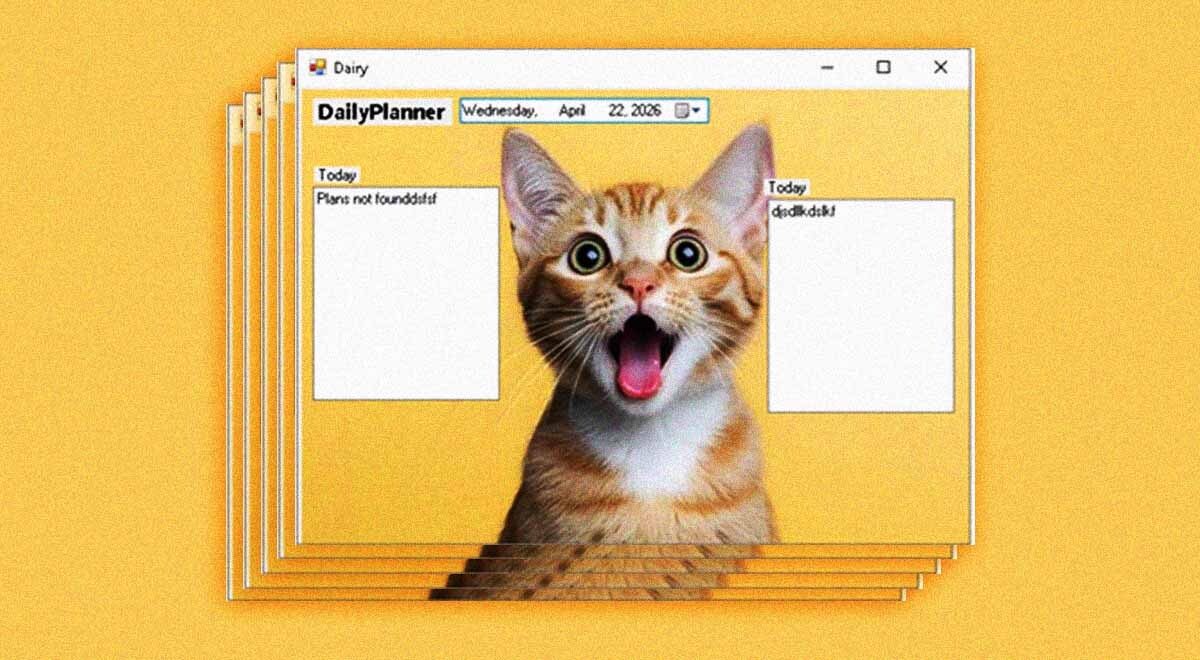
Russian Hackers Disguise Matchboil Spyware as Cat-Feeding Planner
Russian-linked group UAC-0099 is targeting Ukrainian transport, manufacturing, and energy workers with phishing emails that install Matchboil malware, which ESET says hides behind a fake cat-feeding planner.