Cloudflare moves to become a public certificate authority
Twelve years after launching Universal SSL, Cloudflare says it intends to become a public certificate authority: it has applied to the Chrome, Apple, Microsoft and Mozilla root programs and agreed to acquire a broadly trusted root from GlobalSign.
Cloudflare said on September 29 that it intends to become a public certificate authority (CA), though it is not issuing certificates yet. In its Birthday Week news the company reported the first milestones: it has applied for inclusion in the Chrome, Apple, Microsoft and Mozilla root programs, and signed a definitive agreement to acquire a broadly trusted root from GlobalSign, so its certificates reach the widest possible set of devices from day one.
Two paths to trust
A brand-new root is not widely useful for years: even after a root program accepts it, it must propagate into operating systems and devices, and it never reaches the long tail of clients that no longer receive updates. The existing GlobalSign root has been trusted since 2012 and reaches exactly those older clients, while the new root Cloudflare will submit is built for where the ecosystem is heading. Cloudflare wants both.
A new source of free certificates
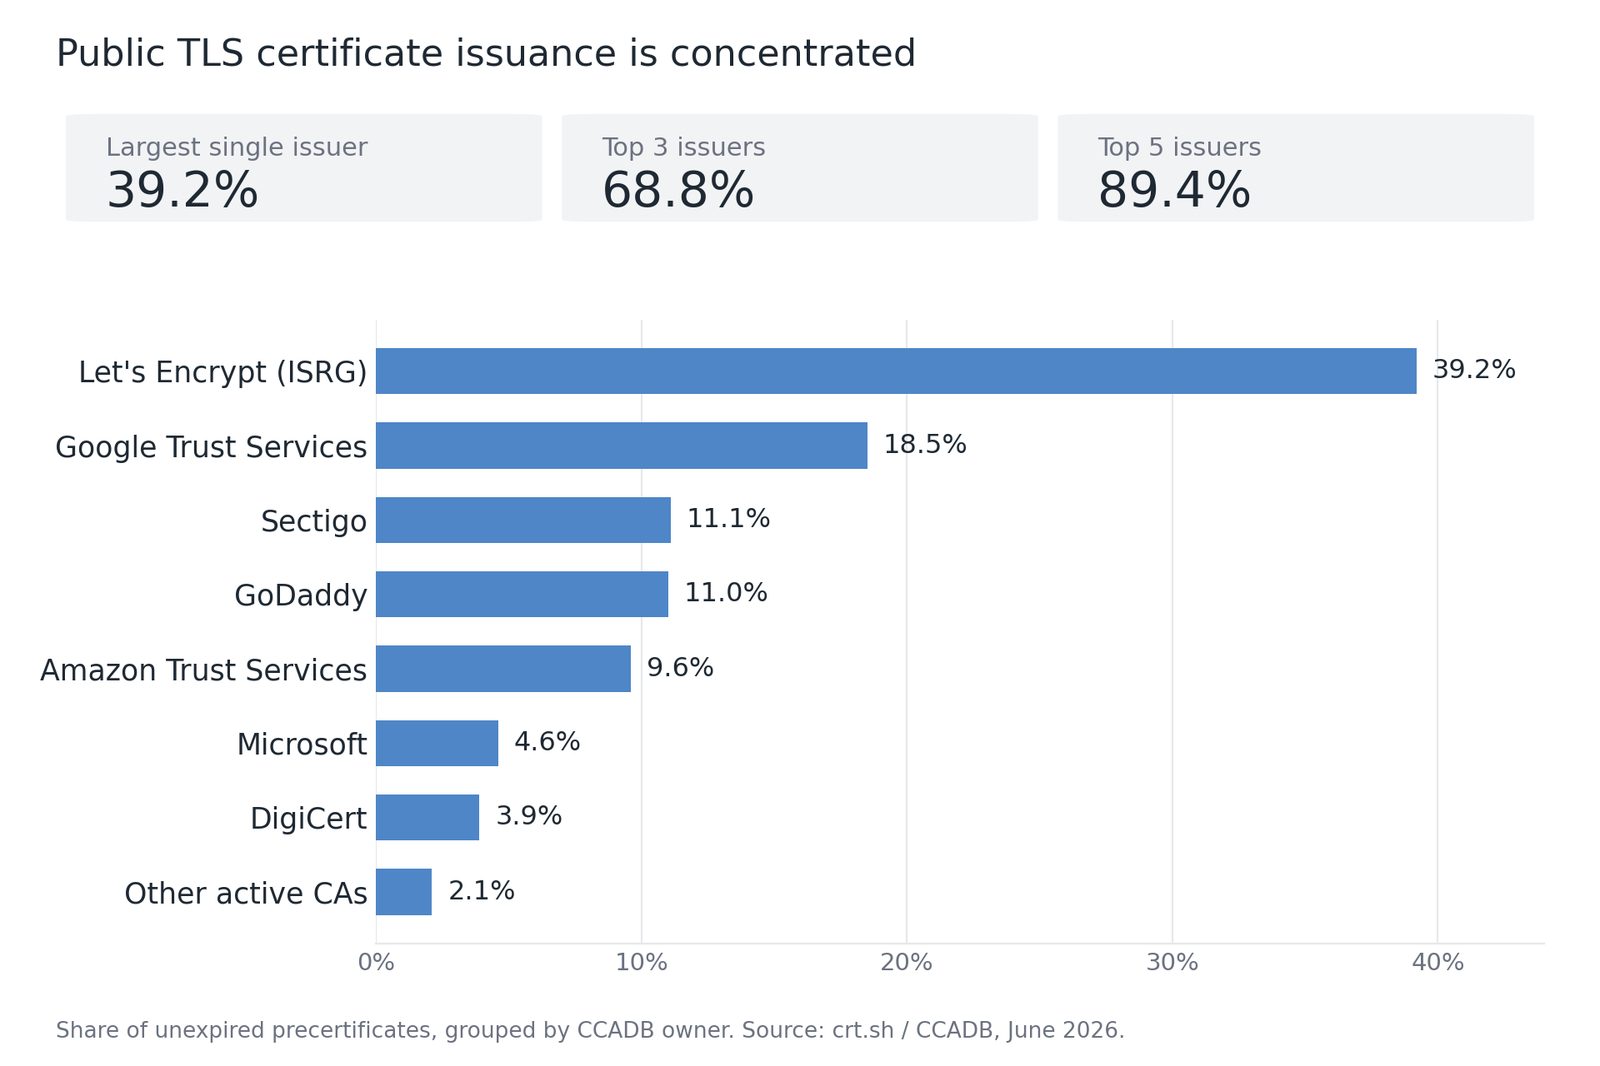
Free, automated certificates now carry most of the encrypted web. Let's Encrypt issues about ten million certificates a day, serves more than 500 million sites and passed four billion active certificates in 2025. Cloudflare calls that concentration a systemic risk. The new CA will be ACME-first, so anyone already using another free CA can move over by changing a directory URL.
Resilience and transparency
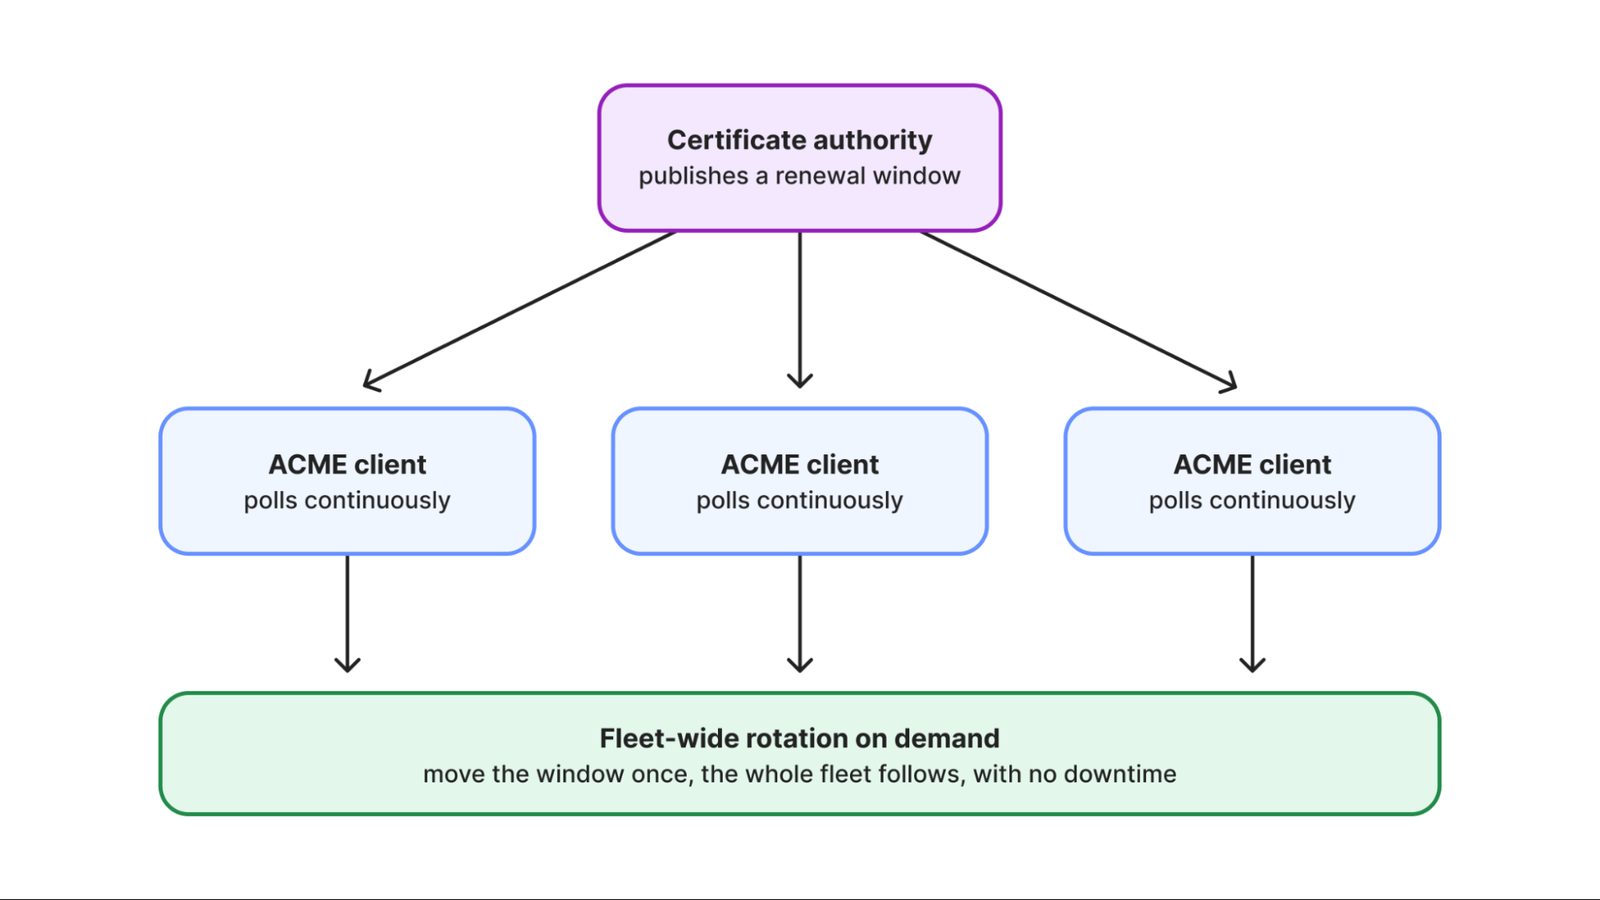
Cloudflare says it will build a CA designed to "fail small" and limit the impact of any single issue. Renewal automation will be a condition of issuance: the CA will only issue to clients that support ACME Renewal Information (ARI), standardized in RFC 9773, and that poll its renewal endpoint. It also promises reproducible builds of its signing software, attestation of its key-holding security modules, and a public dashboard for issuance health.
A post-quantum certificate authority
Cloudflare expects to be one of the first CAs to issue production Merkle Tree Certificates (MTCs), with the first certificates planned for the first quarter of 2027. MTCs deliver publicly trusted certificates in a far more compact form, designed for a post-quantum world where traditional chains strain TLS handshakes; Chrome named them the preferred path for post-quantum authentication this year. One CA will serve both classic certificates and MTCs, letting customers adopt at their own pace.
Cloudflare will act as Customer Zero for the new CA and will keep working with the 16 partner CAs it has relied on for years.
SiTech — AI-powered web development
We build fast, modern websites and bring AI into real business workflows. Have a project or a question? We'd love to help.