Hackers Infect 953 Online Stores With Scanner-Evading JavaScript, Mostly on Magento
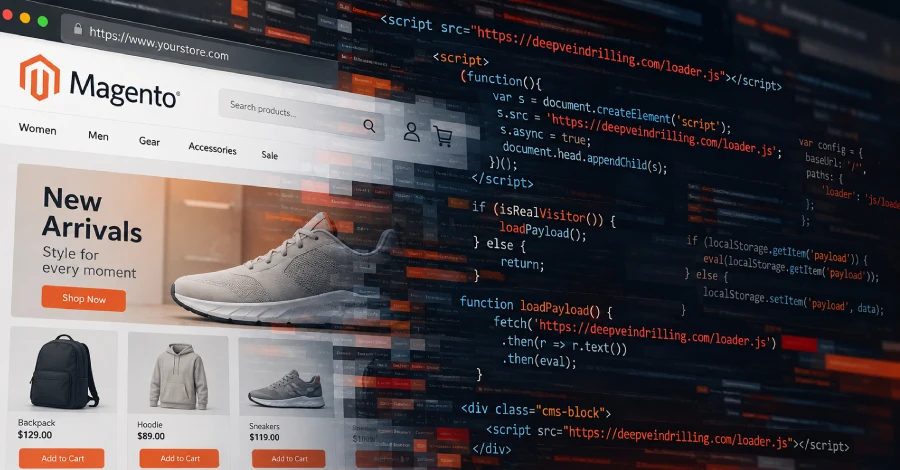
An unknown threat actor infected 953 online stores, mostly running Magento, in a campaign active since July 2025 that uses JavaScript loaders hidden from security scanners, Sansec says.
An unknown threat actor has infected 953 online stores, most of them running Magento, in a campaign active since July 2025, according to Sansec. The attackers insert JavaScript loader code into Magento CMS blocks, and that code reaches only real visitors while staying hidden from security scanners.
Campaign details
Sansec said the malicious code is staged in Magento's cms_block database table, which renders static content into storefront pages. When a shopper opens a compromised site, the CMS block renders and launches attacker-controlled code. The latest loader domain is hosted behind Cloudflare and responds only to script requests from real visitors of infected stores. Sansec found deepveindrilling[.]com in the CMS blocks of 83 online stores since the domain was registered on October 6, 2026. Five domains have been observed over time: manulfie[.]click since July 2025, neswnsssn[.]click since December 2025, lanhd6549tdhse[.]top since March 2026, additionalver[.]com since June 2026, and deepveindrilling[.]com since October 2026.
Loader versions and traffic filtering
Two versions of the loader have been spotted. One stores its payload in the browser's localStorage, so the stashed code can run again on later visits even if the external domain is unavailable. The second adds browser fingerprinting checks to filter out bots and security scanners. Early iterations also used Keitaro as a traffic distribution system, and a request to additionalver[.]com returned "QWE=123;" plus a cookie marking the visitor for 24 hours. The deepveindrilling[.]com version drops Keitaro and builds bot filtering into the loader itself.
Initial access and defenses
Sansec estimates 471 Magento stores were injected through the PolyShell vulnerability, CVE-2026-48356. Another 102 stores had files uploaded through PolyShell or SessionReaper, CVE-2025-54236. In one case, a Magento 2.4.7-p1 store had PolyShell webshells disguised as PNG images and still lacked APSB26-73, Adobe's PolyShell fix. Another Magento 2.4.7-p10 store with no missing core patches was compromised in order to add a rogue administrator account and then use it to inject the code. Site owners are advised to audit suspicious accounts and unexpected CMS blocks in the cms_block and cms_page tables, keep sites updated, and enforce strong passwords.
PHP2Shell context
The disclosure comes as PHP2Shell, two critical PHP vulnerabilities CVE-2026-109618 and CVE-2026-109619, sees widespread exploitation attempts. Perplexity researcher Adel Karimi recorded what appears to be the first in-the-wild successful exploitation of the flaws to run shell commands on honeypot servers. Observed commands used wget, curl, or PHP CLI to fetch payloads from 162.35.99[.]94:80, with no second-stage artifacts observed so far.
Sources: The Hacker News
SiTech — AI-powered web development
We build fast, modern websites and bring AI into real business workflows. Have a project or a question? We'd love to help.