Cloudflare adds post-quantum encryption visibility for individual domains
Cloudflare has added post-quantum cryptography visibility to Logpush, Log Explorer and the HTTP Traffic Analytics dashboard, letting customers see which key exchange algorithm their domains actually negotiate.
Cloudflare on September 29 introduced new post-quantum (PQ) cryptography visibility tools across its Application Security and Logs products. Customers can now inspect and graph the adoption of post-quantum TLS 1.3 encryption for live traffic directly within Logpush, Log Explorer and the HTTP Traffic Analytics dashboard.
The platform surfaces the key exchange algorithm negotiated on every incoming request, which is new at the domain level. Cloudflare has long reported the TLS version in use but not the cryptographic algorithms negotiated with it, so there was no per-domain answer on how much traffic is post-quantum protected.
Why it matters now
Cloudflare is targeting 2029 for full post-quantum security, while its customers work towards quantum-readiness deadlines around 2030. According to Cloudflare Radar, about 70% of browser-generated traffic reaching its network is already protected with post-quantum encryption using hybrid ML-KEM, while only about 15% of the origins Cloudflare connects to use it.
Post-quantum encryption defends against harvest-now-decrypt-later attacks, in which an adversary collects data today and decrypts it later once powerful quantum computers exist. In 2024 NIST said RSA and elliptic curve cryptography should be deprecated by 2030.
What the new dashboard card shows
In TLS 1.3, X25519MLKEM768 is the only recommended algorithm for post-quantum encryption and is preferred by most major browsers. The hybrid approach runs ECDHE over the X25519 curve together with the post-quantum ML-KEM mechanism, so the connection stays secure as long as one of the two holds.
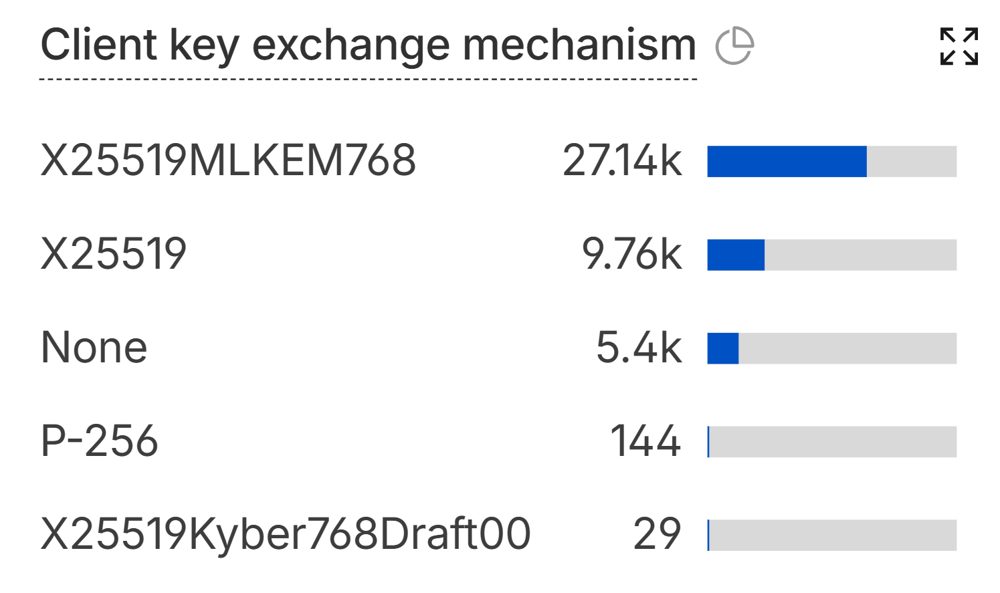
A new TLS Key Exchange card breaks traffic down by group. On Cloudflare's own test domain most traffic uses X25519MLKEM768, some uses classical ECDHE over X25519 or P-256, and the "None" bucket covers RSA key agreement or no TLS at all.
Logs and origin servers
Logpush gains a ClientTLSKeyExchangeGroup field in the HTTP Requests dataset, exposing the negotiated algorithm on individual log lines, while OriginTLSKeyExchangeGroup covers the Cloudflare-to-origin connection. Legacy origins that cannot support post-quantum cryptography can sit behind Cloudflare Tunnel, which carries traffic over TLS 1.3 with X25519MLKEM768 without upgrading the origin.
Cloudflare is also working on post-quantum authentication: origins can already connect with ML-DSA-44 certificates over TLS 1.3, and the company announced a certificate authority that will support post-quantum Merkle Tree Certificates, although encryption remains more widely deployed. Customers with no X25519MLKEM768 traffic should confirm TLS 1.3 is enabled, because there is no separate post-quantum switch.
SiTech — AI-powered web development
We build fast, modern websites and bring AI into real business workflows. Have a project or a question? We'd love to help.