Six Unpatched Danfoss Refrigeration Controller Flaws Allow Remote Takeover
Researchers found six unpatched flaws in Danfoss AK-SM800A refrigeration controllers that let remote attackers take over devices without login. No patch exists; firmware 5.4.0 does not fix them.
Researchers from Midnight Blue discovered six unpatched vulnerabilities in Danfoss AK-SM800A refrigeration controllers that could allow remote attackers to take over devices without authentication. The affected firmware includes the latest version 5.4.0, and no patch has been released.
Vulnerability Details
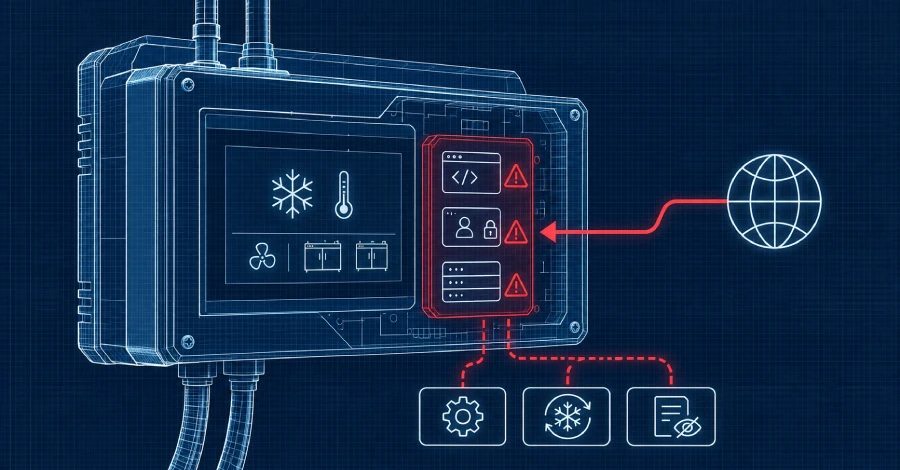
Five of the flaws reside in web request handlers that do not require a login and run as root. The sixth flaw is in the gateway that enforces Strict mode, a login protection that requires encrypted connections and session tokens. When Strict mode is enabled, the gateway flaw can crash it, and the crash could be turned into code execution with more work. The controllers lack secure boot, so an attacker could plant persistent code that survives a factory reset or firmware update.
Agency Guidance
Cybersecurity agencies in Belgium, Ireland and Germany have advised operators to remove the management interfaces of AK-SM800A controllers from the internet. The Belgian and Irish agencies state that updating firmware, changing default passwords or enabling Strict mode alone is not sufficient. They recommend using a secure VPN or protected internal network for remote access and checking temperature setpoints, defrost schedules, alarm settings, user accounts and remote access settings for unauthorized changes.
Vendor Response
Danfoss lists firmware 5.4.0 as the newest release but its release notes do not mention a fix for the six flaws. The vendor's advisory page shows no advisory for these vulnerabilities and no date for a fix. Danfoss previously fixed other flaws in the AK-SM800A in 2023 and 2025, but the firmware version 5.3.2 the researchers examined, then the newest, is newer than all of those fixes.
Impact and Recommendations
Attacks on these controllers in France and across Europe have caused unwanted defrost cycles and stock loss. The German BSI says it has no information about any exploitation of the six new flaws in those incidents. Researchers warn that the code base likely contains more similar issues and that patching flaws one by one or relying on Strict mode misallocates scarce security resources. Operators should prioritize removing internet exposure before a patch becomes available.
Sources: The Hacker News
SiTech — AI-powered web development
We build fast, modern websites and bring AI into real business workflows. Have a project or a question? We'd love to help.