Blog
Articles about web development, AI, and technology
60 articles · 17 tags · 15 connections
Drag · tap a tag to filter articles
3 articles · Page 1 of 1
•SiTech AI Team
Debian APT Security Update Fixes CVE-2026-109518 in trixie
Debian published DSA-6607-1 for apt, covering CVE-2026-109518. A man-in-the-middle attacker could replace a verified package after an HTTP redirect and run code as root. The stable trixie release is fixed in apt 3.0.4.
•SiTech AI Team
Fedora Linux 45 Released With Stratis Installer Support
Fedora Linux 45 is available with polished desktop upgrades, Stratis storage support in Anaconda, updated toolchains, and migration guidance for retiring NetworkManager VPN plugins.
•SiTech AI Team
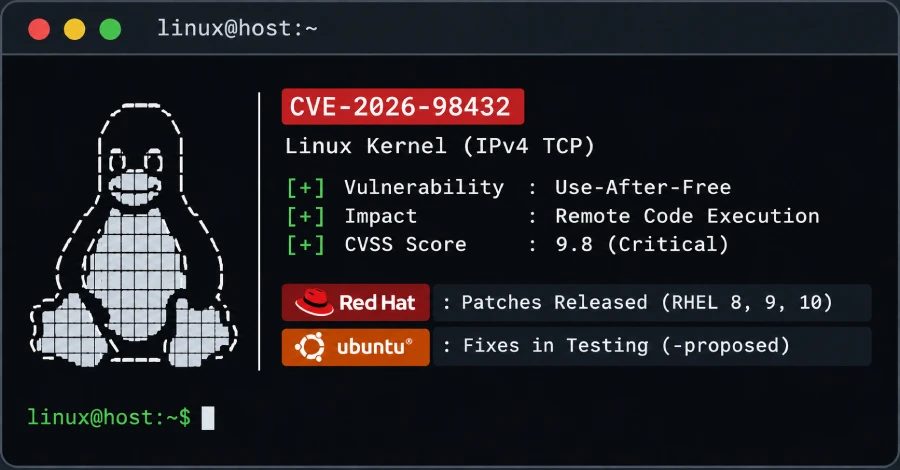
Red Hat Patches 9.8-Rated Linux TCP RCE Flaw While Ubuntu Releases Fixes for Testing
Fixed kernels for CVE-2026-98432 are available for RHEL 8, 9 and 10, while Ubuntu fixes for 22.04, 24.04 and 26.04 LTS remain in -proposed testing. The flaw allows remote, unauthenticated code execution.