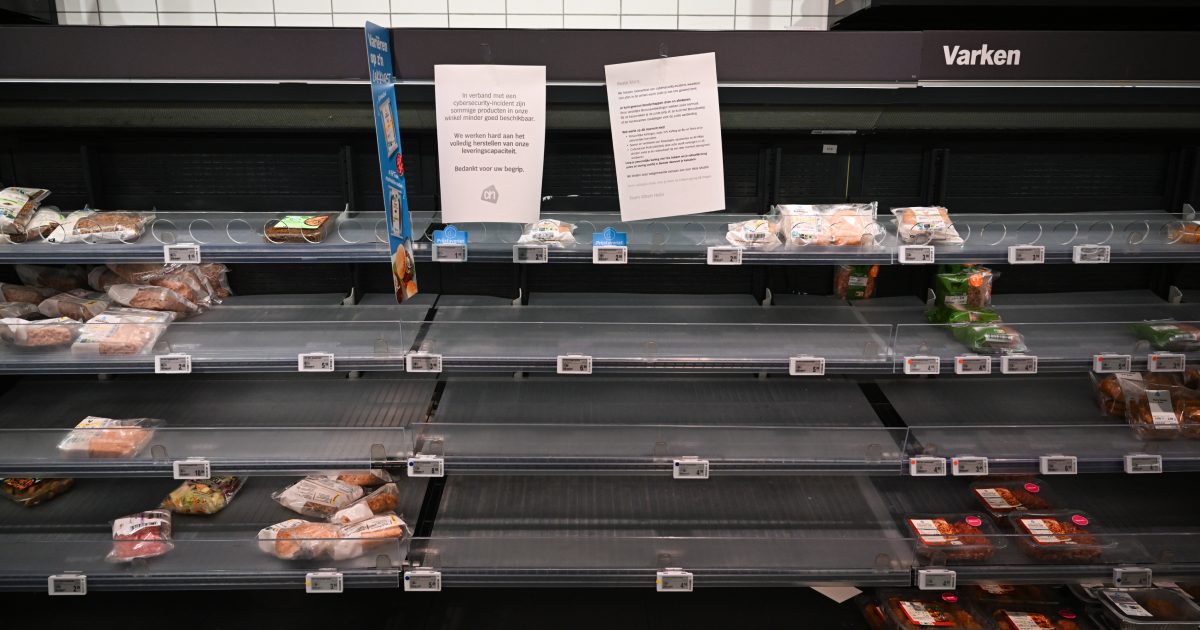
Russia-linked hackers exploit poorly secured industrial systems in the West, Bloomberg reports
Bloomberg reports that Russia-linked hackers are exploiting poorly secured industrial systems to sabotage factories, utilities, water facilities and food production across the West, causing pipes to burst, food to spoil and fires.
Russia-linked hacker groups have been exploiting poorly secured industrial systems to sabotage factories, utilities, and food production across the West, Bloomberg reported in a lengthy feature. The attacks have targeted water facilities, factories, and food companies and have caused pipes to burst, food to spoil, and fires to break out.
Incidents in Europe
In Spain, crematorium ovens at a funeral home in Alicante province stopped working, and equipment at a transformer factory in Catalonia malfunctioned and a fire broke out. Two wineries halted operations after heating and ventilation systems were disrupted. The incidents took place from late 2024 to the summer of 2026.
In mid-December 2024, 450 homes in the Danish village of Tureby lost their water supply after the pressure setting in the electronic control system was turned to zero. Workers restarted the pumps, but the next day pressure surged and underground pipes burst and leaked. Jan Hansen, who chaired the committee managing the local water supply, found that he could no longer access the control panel. Technicians from Evotect ApS, the pump controller manufacturer, determined the system had been hacked. Hansen later admitted the water supply used a cheap system and that its password was 1234.
United States incidents
In 2024, hackers shut off refrigeration at a meatpacking plant near Los Angeles, spoiling more than 2,000 pounds (about 900 kilograms) of meat and forcing workers to evacuate after an ammonia leak. That year, hackers attacked a public water system in Texas and changed control settings, causing an unknown volume of drinking water to spill from storage tanks. In October, hackers broke into a waste treatment facility control system in Pennsylvania and tampered with equipment used to kill bacteria.
Groups and suspects
Cyber Army of Russia Reborn, or CARR, is linked to Russia's military intelligence agency, formerly known as the GRU. It has claimed responsibility for attacks in Europe and the United States, including on water systems in the United States and Poland and a power plant in France. Z-Pentest was formed in September 2024 by members of CARR and NoName057(16). The U.S. Cybersecurity and Infrastructure Security Agency said some CARR members broke away and formed a group focused on industrial sabotage. The European Union holds Z-Pentest responsible for attacks on critical infrastructure, particularly in energy and water.
The U.S. Justice Department accused Ukrainian citizen Victoria Dubranova in late 2025 of participating in cyberattacks on Russia's behalf. She has been charged with working for CARR and Z-Pentest, is in custody, and denies the charges. She had worked with the hackers since at least the fall of 2022 and was recruited through a chat group for people seeking remote work, according to the Justice Department. Z-Pentest said Dubranova had not engaged in hacking. In March, Italian citizen Chris Barlati was arrested in Spain. Spanish police said he acted as an intermediary for the hackers and helped select targets. He has pleaded not guilty.
SiTech — AI-powered web development
We build fast, modern websites and bring AI into real business workflows. Have a project or a question? We'd love to help.