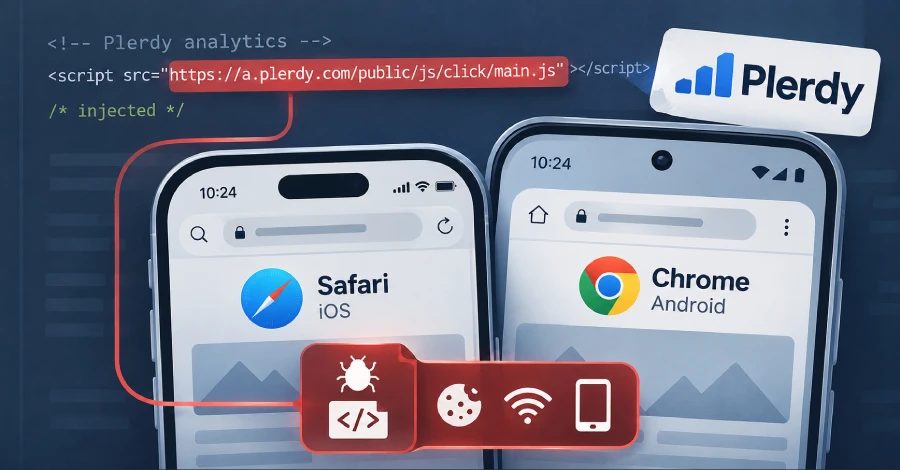
APT29-Linked Hackers Use Hijacked Analytics Script to Target iOS and Android
Sekoia researchers say an APT29-linked campaign named Poisoned Source used compromised websites, lookalike domains and a Plerdy SEO Tracker supply chain compromise to deliver iOS and Android exploit chains.
A threat actor linked to APT29 is said to be behind a large-scale watering hole campaign targeting iOS and Android users through compromised websites, fake domains and a supply chain attack involving the Ukrainian web analytics service Plerdy SEO Tracker. Sekoia researchers Amaury-Jacques Garçon and Félix Aime said the injected JavaScript collects browser and device attributes before infrastructure delivers a platform-specific N-day exploit chain. The campaign, codenamed Poisoned Source, was discovered in mid-October 2026 and aims to serve payloads that steal browser cookies and, in some cases, Wi-Fi passwords or full mobile device data.
Infection Routes
Sekoia identified three infection vectors: compromise of legitimate websites to inject malicious JavaScript; lookalike sites masquerading as high-profile websites in the U.S., Ukraine, Czech Republic and Bulgaria, including america250[.]holiday; and a supply chain compromise of Plerdy SEO Tracker between Aug. 27 and Sept. 3, 2026, by injecting malicious code into a.plerdy[.]com/public/js/click/main.js.
Some compromised sites include a major industry trade association representing U.S. companies in the chemical industry, a far-right European political party and a Bulgarian military-related website. Sekoia said it remains unclear whether attackers intended to target visitors to specific websites or sought to compromise as many unpatched mobile devices as possible. The researchers noted that several sites are likely to attract high-value or strategically important visitors in the context of the Russia-Ukraine war, and that the supply chain attack spread through high-value targets such as army, special forces and military equipment websites.
Exploit Chains
All methods lead to a JavaScript loader that profiles the visitor's device and browser, then serves appropriate next-stage malware. For iOS users, it leads to an exploit kit called DarkSword to harvest cookies and full device data. On Android, the malware is equipped to exfiltrate Chrome data and Wi-Fi passwords without establishing persistence.
The researchers identified three exploit classes. Class A targets iOS devices running iOS 16.7 and exploits CVE-2025-43529 and CVE-2024-27834 to deliver JavaScript malware for cookie theft. Class B targets iOS devices running iOS 18.5 and exploits the DarkSword exploit chain comprising CVE-2025-43529, CVE-2026-20700, CVE-2025-14174, CVE-2025-43510 and CVE-2025-43520 to deliver JavaScript malware for full device data exfiltration. Class C targets Android devices running Chrome versions from 139 through 145, excluding version 143, and exploits CVE-2026-3910 and CVE-2025-27038 to achieve remote code execution, sandbox escape, privilege escalation and delivery of AndroSnitch to collect Chrome data and Wi-Fi passwords.
In all three cases, exfiltrated data is sent to ad.starx-net[.]com:8881/telemetry/v12. The Android attack chain checks whether the targeted device is a Samsung Galaxy S25 Ultra by examining its model identifier, SM-S938B, and terminates exploitation if the device matches.
Sources: The Hacker News
SiTech — AI-powered web development
We build fast, modern websites and bring AI into real business workflows. Have a project or a question? We'd love to help.