Google Warns of Renewed Oracle PeopleSoft Exploitation via WAF Bypass
Mandiant says the ShinyHunters-linked UNC6240 group is mass-exploiting CVE-2026-35273 again, dodging WAF rules by URL-encoding a single character in the request path and dropping JSP web shells on victim servers.
Renewed mass exploitation
Google is warning of renewed mass exploitation of a critical Oracle PeopleSoft vulnerability, CVE-2026-35273 (CVSS score: 9.8), which allows unauthenticated remote code execution.
Mandiant links the activity to UNC6240, a group tied to ShinyHunters. The flaw was first abused as a zero-day in attacks on academic institutions; Mandiant then notified more than 100 organizations whose endpoints matched vulnerable IP addresses.
Bypassing the WAF rules
"This new wave of activity stems from UNC6240 modifying its exploit to bypass web application firewall (WAF) rules blocking the vulnerable Environment Management Hub (PSEMHUB) endpoint," Mandiant said.
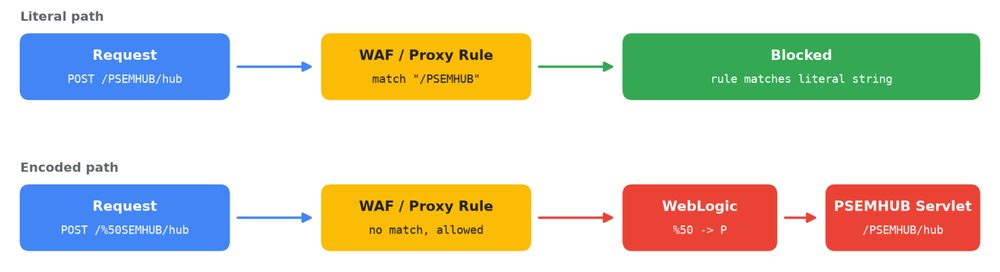
The group bypassed the string-based rules by URL-encoding a single character in the request path, requesting /%50SEMHUB/ instead of /PSEMHUB/. Many WAF and reverse proxy rules match the literal path before URL decoding, while the PeopleSoft application server decodes the request and routes it to the vulnerable servlet.
The full attack chain
The chain starts with POST requests to /%50SEMHUB/hub carrying a serialized Java object, used to identify susceptible targets. The attackers then abuse Java deserialization to deploy web shells and run commands without writing files to disk.
Two JSP web shells are dropped in the PSEMHUB.war directory: x.jsp enables command execution, while u.jsp allows chunked file uploads and command execution via cmd.exe. Attackers use u.jsp to upload a valid, signed but trojanized installer, Ple64.exe, which loads in memory SIDEEYE, a C++ backdoor.
SIDEEYE talks to 162.219.30[.]165 over TCP and provides credential theft from browsers and desktop applications, process and file management, an interactive reverse shell and a reverse proxy. About a quarter of UNC6240's commands ran as root or NT Authority\SYSTEM.
Mitigation and extortion risk
Google recommends patching CVE-2026-35273, disabling the Environment Management Hub service in multi-server setups or removing the PSEMHUB application in single-server ones, searching WebLogic access logs for "/PSEMHUB/" and percent-encoded variants, and inspecting PSEMHUB.war for JSP web shells.
Companies should also check temporary directories for large archive files and review database audit logs for bulk queries against HR and payroll records.
Google says UNC6240 is known for data theft extortion, so victims should expect extortion attempts. Separately, ShinyHunters claims it breached the FBI's FBIJobs.gov portal using a different PeopleSoft zero-day and stole 2-3 TB of data; the group says it is not seeking a ransom.
SiTech — AI-powered web development
We build fast, modern websites and bring AI into real business workflows. Have a project or a question? We'd love to help.