Cloudflare's CryptoLabe uses AI to chart its post-quantum migration
Cloudflare has detailed CryptoLabe, an internal AI tool that scans its repositories to find where classical cryptography is still in use and to surface blockers ahead of its 2029 post-quantum target.
Cloudflare has detailed CryptoLabe, an internal tool that uses large language models to find every use of cryptography in its codebase as the company works toward full post-quantum readiness by 2029. It is named after the mariner's astrolabe.
The scale of the problem
Most Cloudflare products sit in one source-control platform, but the code spans many repositories and cryptography hides in imported libraries that may never be called and in protocol defaults such as a TLS 1.3 listener negotiating classical X25519 instead of hybrid X25519MLKEM768. Pattern matching is not enough: searching for RSA or X25519 overcounts unused code, undercounts defaults, and cannot say how a key is used.
How CryptoLabe works
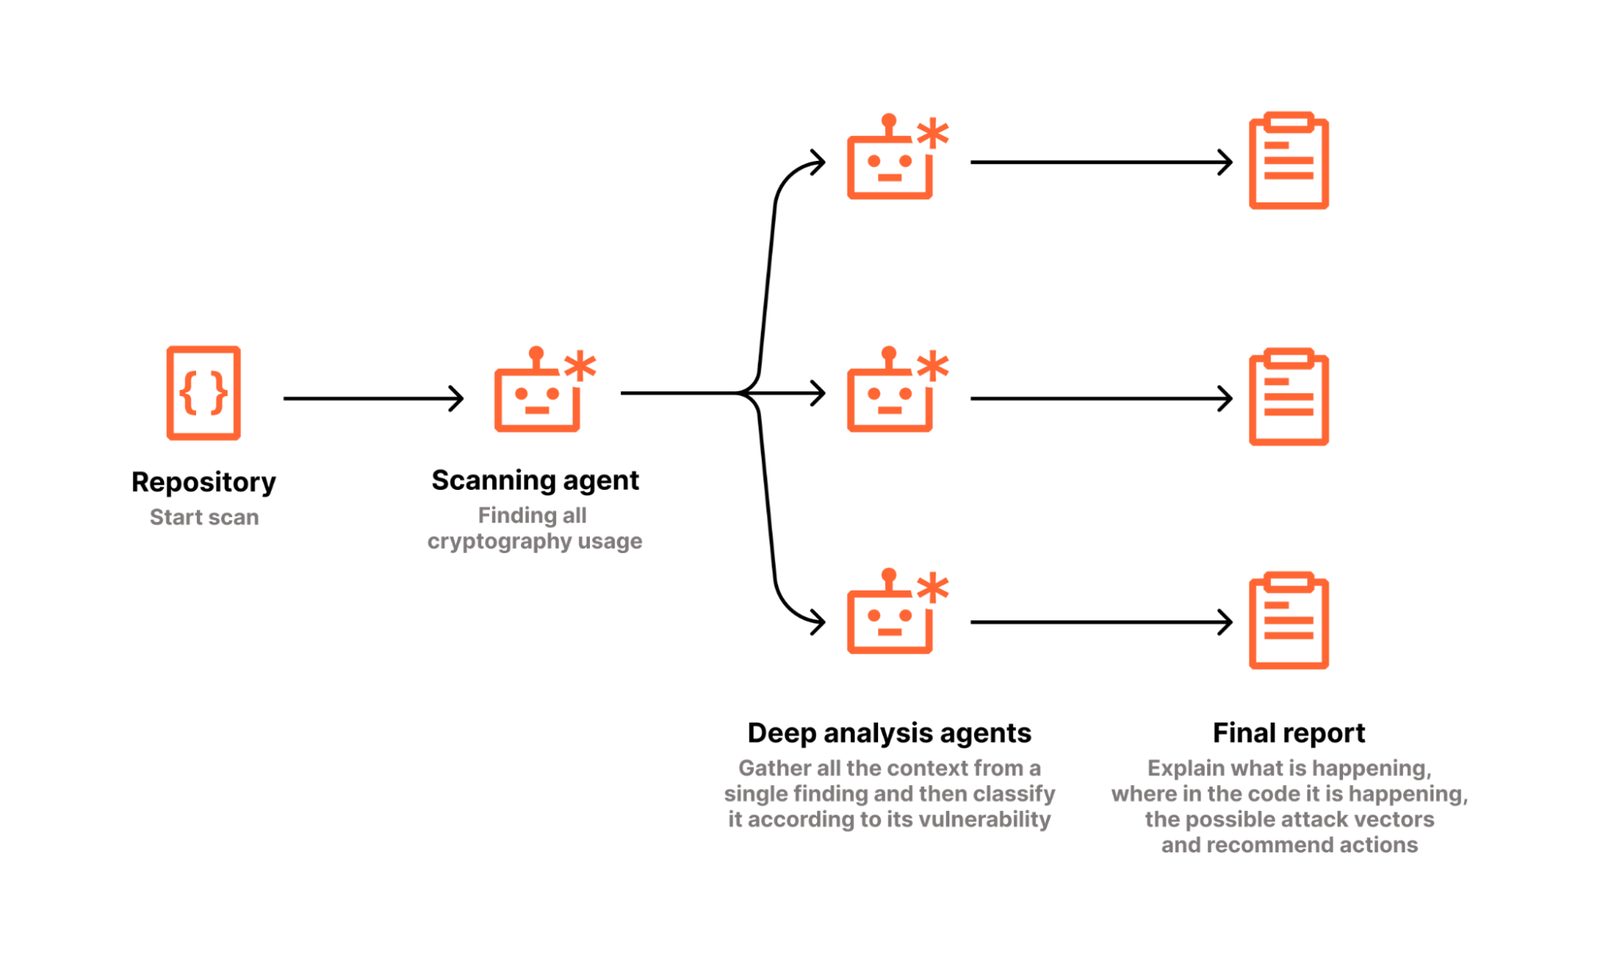
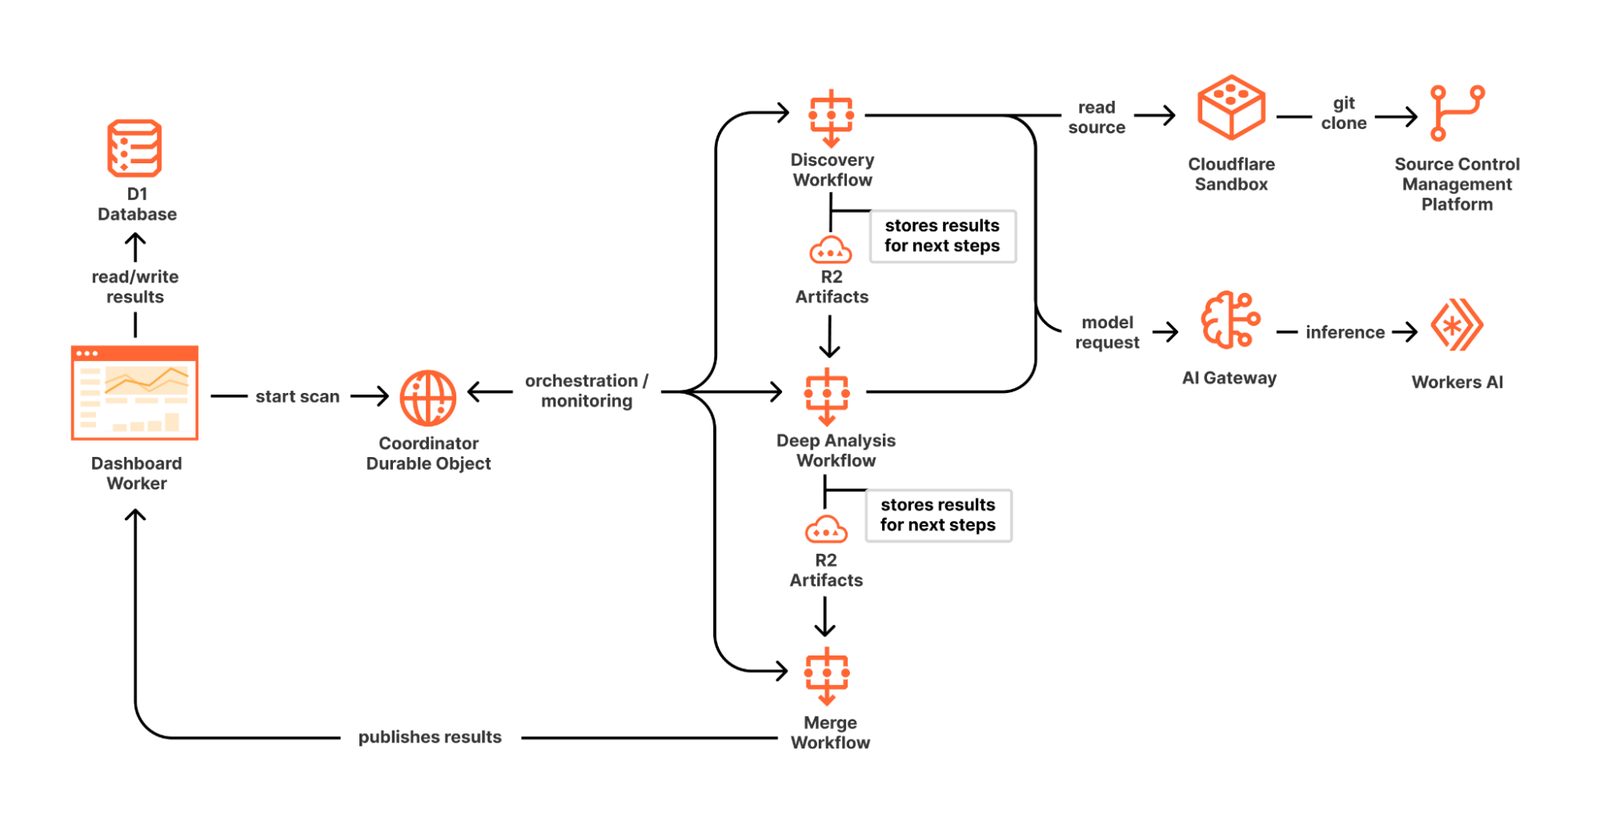
A discovery stage maps the repository and searches source, configuration, tests and documentation for key agreement, signatures, public-key encryption, tokens and hardware-security-module integrations, producing "raw observations". An analysis stage rechecks each finding and classifies it: classical encryption, classical signature, classical token, PQ-ready hybrid key exchange or PQ-ready. When evidence is thin, it answers "more evidence needed", "external dependency" or "unknown" rather than guessing. It runs on two Workers with a D1 database, with Cloudflare Workflows driving each scan.
Prerequisites and hard cases
CryptoLabe groups findings by "prerequisite": work one product team cannot do alone. The blog shows six findings that depend on post-quantum SAML, the single sign-on protocol. A separate prompt hunts "hard cases": custom protocols, signatures in size-constrained fields, hardware cryptography and parties without post-quantum support. One is a certificate in an HTTP header, where a fixed-size assumption may break because post-quantum certificates are larger.
What other teams should do
Cloudflare says most organisations should not inventory every cryptographic operation they own, calling it a waste of resources now, and suggests starting with one important repository, validating findings with the owning team and prioritising what can be fixed and what is blocked. Selected prompts are on GitHub. Cloudflare deployed X25519MLKEM768 in TLS 1.3 in 2022, before the standard was final.
SiTech — AI-powered web development
We build fast, modern websites and bring AI into real business workflows. Have a project or a question? We'd love to help.